Policy Didn't Stop These Breaches. Judgement Would Have.
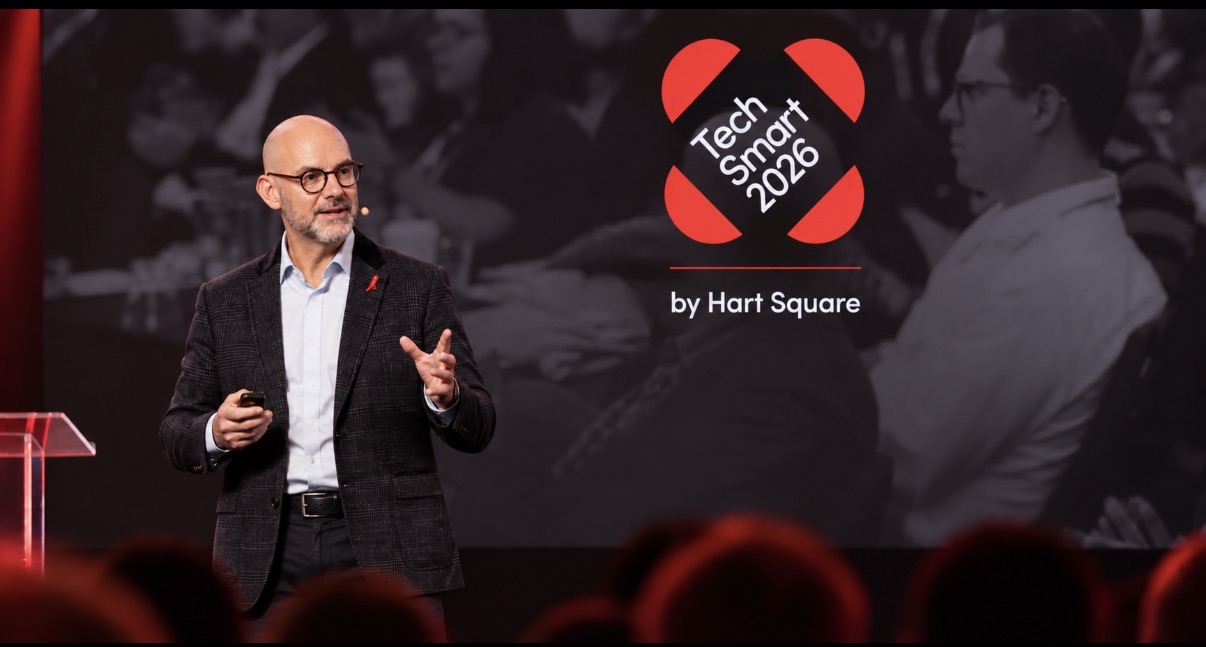
I stood up at TechSmart 2026 this week and told a room full of charity leaders something they already suspected but hadn't quite said out loud: almost every charity in the country now has an AI policy sitting in a folder somewhere, and almost every charity still has staff pasting sensitive data into ChatGPT without a second thought. Both things are true at the same time, in the same organisation, and once you notice that, a lot of what we're taught about governance stops quite making sense.
Why this matters right now
Three quarters of UK charities, 76 percent, are already using AI in some form. That's not a forecast, that's now. Only around half have a policy governing that use, which is actually good news, because two years ago that figure was just 6 percent. The sector is catching up fast. But Microsoft's own research, published last October, found that 71 percent of UK employees use AI tools their employer hasn't approved. Put those numbers together and you get a very specific picture. Adoption has raced ahead, policy is catching up slowly, and the gap between the two is being filled right now by individual staff making individual decisions, with no guidance, no visibility, and the best of intentions.
Three breaches, three policies that didn't help
I walked the room through three real cases. Mermaids, the charity supporting transgender and gender diverse young people, had its email settings misconfigured in a way that exposed confidential information for years, and was fined £25,000 by the ICO. Five household name charities, including Friends of the Earth, Dogs Trust and the RSPCA, had donor data compromised when hackers breached Kokoro, a sub-contractor working for a survey supplier several of them shared. And Blackbaud, a fundraising platform used right across the sector, was hit by ransomware, affecting over a hundred organisations worldwide including the National Trust here in the UK.
Every one of these organisations had data protection obligations and processes in place before the breach happened. Not one policy stopped it. That's not an argument against having a policy, you should absolutely have one. It's an argument against believing the policy is where the work ends. A policy tells you what should happen. It has no way of being there when someone actually decides what to do.
Data governance has become a judgement problem
I'd argue this is the real shift happening in the sector right now. It used to be enough to write the rulebook, circulate it, and get everyone to sign that they'd read it. That worked when the risks were relatively static. AI has changed the shape of the problem, because now the moment where governance either holds or doesn't is happening dozens of times a day, at someone's desk, in the three seconds it takes to decide whether to paste a case note into a chat window.
I use a framework I call the 20:60:20 rule to explain this. Twenty percent is your policy and your data classification, necessary but not sufficient on its own. Sixty percent is the tool itself, whether staff are using an approved AI platform with a proper data agreement or a free consumer account nobody vetted. And the final twenty percent is the moment of use, the person mid task, deciding what to paste. Most organisations pour almost all their effort into that first twenty percent, the policy document, and almost none into the last. Given what the case studies show, that's backwards.
A rule simple enough to survive a Tuesday afternoon
The practical fix I gave the room wasn't another training module nobody remembers. It was a traffic light. Green data is public, already published, safe anywhere. Amber is aggregated or anonymised, no names attached, fine inside an approved tool. Red is anything that identifies a real person, names, case notes, safeguarding information, health data, donor details, and it never goes into a public AI tool, full stop. Staff don't need to become GDPR experts. They need something they can apply in three seconds, because three seconds is genuinely all the moment gives you.
There's a leadership dimension to this too. In December 2025 the Fundraising Regulator updated its guidance to make explicit that trustees, not just IT teams, are accountable for how their organisation uses AI in fundraising. That's a meaningful shift. It moves this from a technical policy sitting with a supplier to a governance obligation sitting with the board, the same way safeguarding or financial oversight does. People copy what leaders visibly do far more reliably than they follow what leaders write down.
What to actually do with this
If you run a charity, don't start by rewriting your policy again. Start by asking where the actual decision points are in your organisation this week, the report that gets drafted with AI help, the case file someone wants summarised faster, the donor list someone wants segmented. Then give people a rule they can carry into that moment rather than a document they read once in induction.
Policy protects your paperwork. People protect your data. In a sector handling some of the most sensitive information anyone holds, on some of the tightest budgets anywhere, that distinction has never mattered more.
Frequently asked questions
Why is policy alone failing to prevent data breaches in charities?
Policies tell staff what should happen, but they cannot intervene when someone makes a quick decision at their desk. Real cases show organisations had data protection processes in place that failed to stop breaches. Data governance has become a judgement problem, with staff frequently deciding in seconds whether to paste sensitive information into unapproved AI tools.
What is the 20:60:20 rule for charity AI governance?
The 20:60:20 rule splits governance into three areas: twenty percent is policy and data classification, sixty percent is using approved tools with proper data agreements, and twenty percent is the moment of use. Most charities overinvest in writing policy, but neglect the critical moment when staff decide what to paste into AI tools.
How does the traffic light system for AI data usage work?
The traffic light system gives staff a three-second rule: green data is public and safe anywhere, amber data is aggregated or anonymised for approved tools, and red data includes identifiable personal details, health data, or donor information. Red data must never be entered into public AI tools under any circumstances.
How widespread is AI usage across the UK charity sector?
Three quarters of UK charities, or 76 percent, currently use AI in some form. While policy adoption has risen from 6 percent two years ago to around half of charities today, 71 percent of UK employees still use unapproved AI tools. This creates a gap where unguided staff make individual data decisions daily.
What are charity trustees accountable for regarding AI governance?
Following guidance updated by the Fundraising Regulator in December 2025, trustees are explicitly accountable for how their organisation uses AI in fundraising. This shifts AI governance from being seen as an IT technical issue to a board level duty, making trustee oversight similar to existing obligations for financial management or safeguarding.
You may also be interested in
Four Reasons to Adopt AI
Four reasons businesses give for waiting on AI, and why each one turns into a stronger case for starting now. From the opportunity gap to why trust can improve, not erode.
What did the task you just automated used to teach the person doing it?
I ask business owners how much time AI has saved their team, and they always have a number ready. I ask what the task used to teach the person doing it, and the room usually goes quiet.
Never miss an article
Get new articles by email
Whenever I publish something new on AI, cybersecurity and cyber resilience, I'll send you a link. No newsletters, no selling, and one click to stop at any time.
Your address is used only to send you new articles. See the privacy notice.